Universal Guidance Engine — Onboarding Tours SDK
A self-hosted platform for product tours, tooltips and checklists, with a dependency-free JavaScript SDK that plugs into four different web apps.
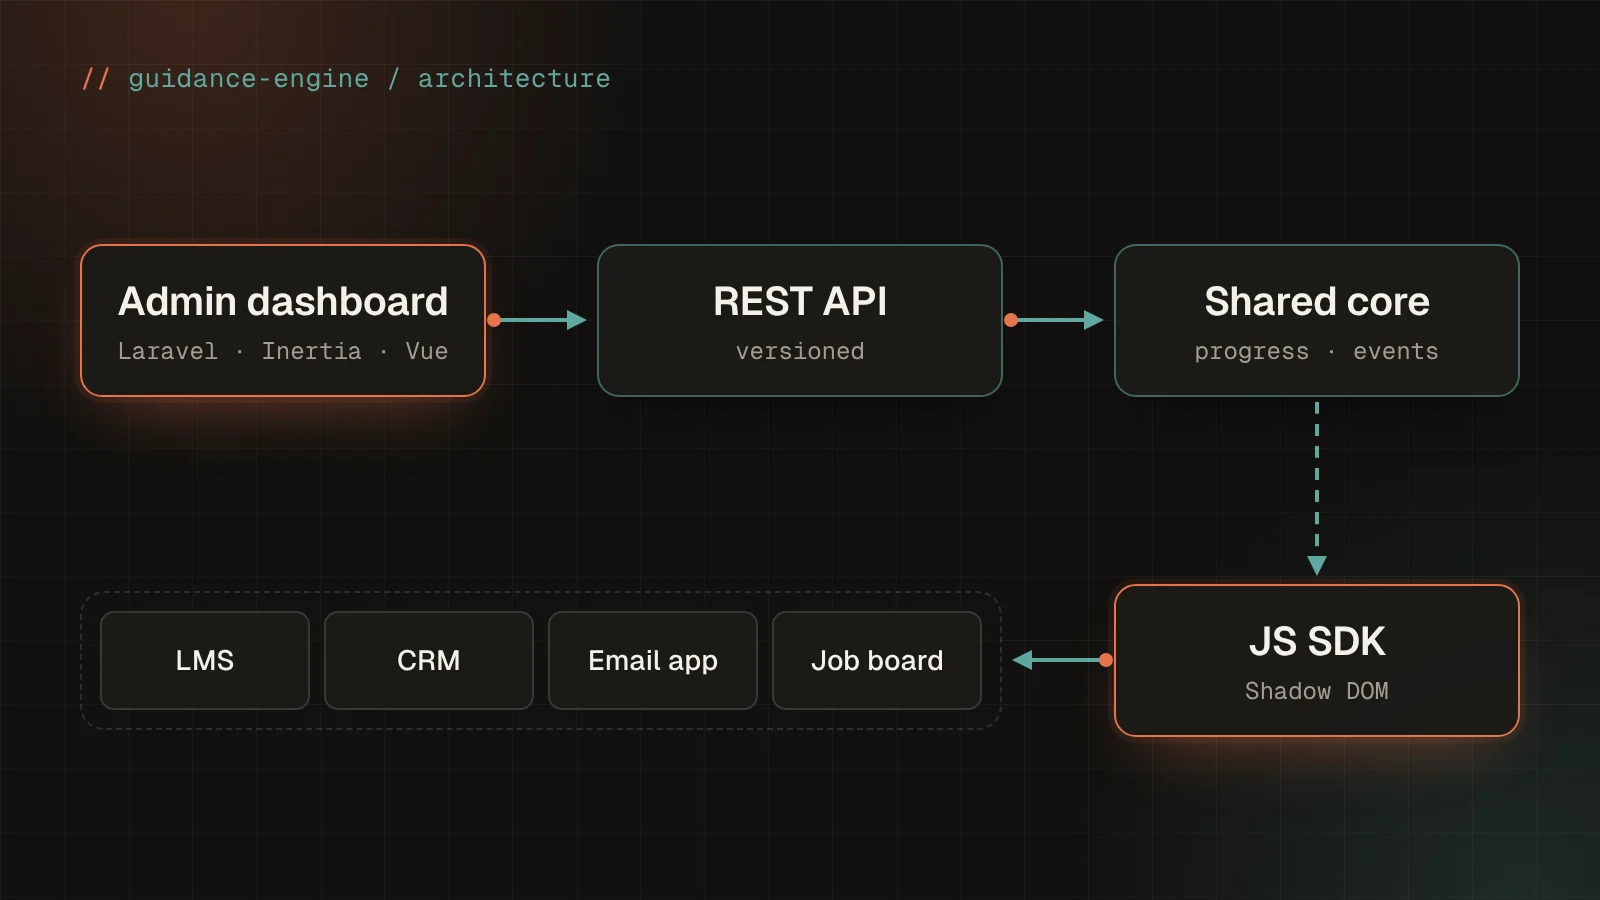
Overview
An internal onboarding and guidance platform: admins build tours, tooltips and checklists in a Laravel + Inertia + Vue dashboard, and a framework-agnostic JavaScript SDK shows them inside any web application. It ships with drop-in integrations for an LMS, a CRM, an email-marketing platform and a job board.
The Problem
Each product needed its own onboarding, and building it separately in every app is slow and inconsistent. The business needed one engine that could guide users in several unrelated applications.
Solution
One shared core tracks user progress and events for all guidance types. A versioned REST API serves content, and a vanilla-JS SDK renders it inside a single Shadow DOM root so it never clashes with the host app’s styles. Host apps are just rows in an applications table, so none of them is a hard dependency.
Architecture
Key Features
- →Tours, tooltips and checklists from one shared core
- →Dependency-free embed SDK rendered inside Shadow DOM
- →Allow-list sanitisation of rich text before rendering (XSS-safe)
- →Audit log for every publish, draft, archive and config change
- →Canonical business events wired into each host app
Tech Stack
Key Decisions & Challenges
Running inside apps you don’t control
Host apps have their own CSS and scripts. Rendering the SDK inside a Shadow DOM root isolates its styles completely, and keeping it dependency-free avoids version conflicts.
Security of admin-authored content
Tour content is rich text written by admins and injected into other apps. Everything is sanitised against an allow-list before it reaches the page, with tests covering known XSS vectors.
Testing & Quality
- ✓Full Laravel test suite, including integration tests for all 4 host applications
- ✓Dedicated security and access-control tests
- ✓XSS sanitiser tests against known attack vectors
Lessons Learned
- →Treating integrations as data, not code, keeps a platform generic
Results
MVP complete and handed over with documentation for installation, deployment and event wiring, integrated with four host applications.
What I'd Do Differently
- ↻Publish the SDK as a versioned npm package from day one
Need something similar?
I can build a system like this for your business — tell me what you need and I'll reply with a plan and a quote.